
Bitcoin has successfully executed a quantum-resistant transaction on its mainnet without modifying its underlying consensus rules, demonstrating that certain holders could potentially move funds away from future quantum vulnerabilities ahead of an official protocol upgrade.
Completed on Aug. 26, the transaction relied on a design created by StarkWare researcher Avihu Levy that replaces elliptic-curve signatures with hash-based security. Block 964,199 included the transaction after it was sent directly to Bitcoin miner MARA utilizing its Slipstream service.
StarkWare highlighted the transfer as the initial quantum-safe spend on the Bitcoin mainnet. While past experiments investigated post-quantum techniques via Bitcoin Script and Blockstream’s Liquid sidechain, this test proved that the Bitcoin network itself can process a hash-based spending mechanism without altering consensus rules.
Still, this workaround does not render Bitcoin fully quantum-safe.
Eli Ben-Sasson, Chief Executive of StarkWare, cautioned that the test should not be viewed as proof that Bitcoin is presently ready for quantum computing. He emphasized that more comprehensive soft-fork solutions are still required to safeguard the entire network at scale.
While noting that “A quantum-safe Bitcoin tx on mainnet” confirms that viable strategies exist, Ben-Sasson stressed that the primary objective is creating a migration path before quantum machines gain the capability to compromise exposed keys.
How Quantum-Safe Bitcoin operates
For numerous Bitcoin addresses, public keys stay concealed behind a hash until the owner initiates a spend. This temporal gap is critical because an oncoming quantum adversary would need to obtain the public key before attempting to figure out the corresponding private key.
The Quantum-Safe Bitcoin (QSB) construction created by Levy leverages this window to transfer eligible coins into a hash-based security framework prior to the exposure of the classical public key.
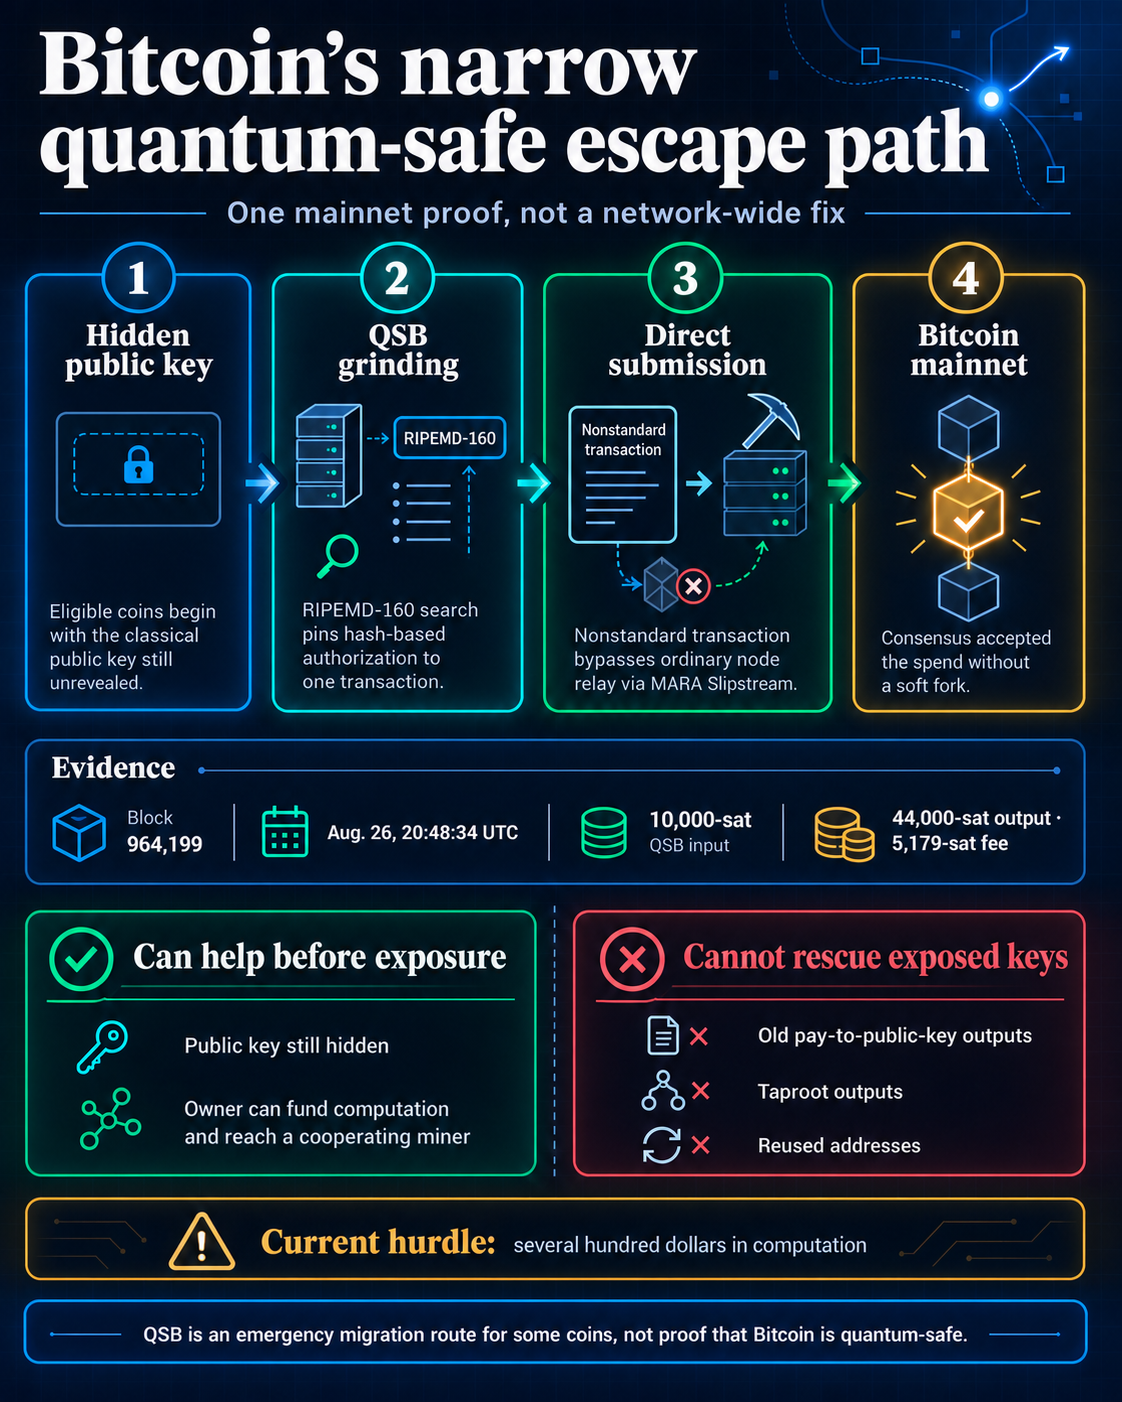
The technique functions by iteratively altering candidate transaction data until it yields a hash that the Bitcoin protocol recognizes as a properly formatted signature. This computation happens prior to broadcasting the transaction, shifting the core security reliance from elliptic-curve cryptography to the computational complexity of reversing hash functions.
Although quantum computers can also speed up attacks against hashes, their advantage is vastly smaller than the capability Shor’s algorithm grants against public-key cryptography. Consequently, QSB offers a prospective transition route for coins whose public keys stay hidden.
This defense mechanism fails to protect coins with already visible public keys. Legacy pay-to-public-key outputs, Taproot outputs, and reused addresses stay vulnerable because a prospective quantum attacker could compromise those keys before the owner finishes migrating.
Furthermore, QSB remains impractical for everyday wallet tasks.
Even though the transaction complies with Bitcoin’s consensus rules, default node policies classify it as nonstandard, meaning it will not naturally propagate across the public mempool. StarkWare had to route the transaction straight to MARA via Slipstream, a dedicated service for processing select nonstandard transactions.
The extensive computing requirements present another obstacle. StarkWare reported that the mainnet trial incurred expenses of several hundred dollars, whereas the open-source repository for the project estimates expenses between $75 and $150 for specific cloud-GPU search configurations.
Because of these limitations, QSB serves as a niche escape hatch for select coin holders rather than a scalable fix for Bitcoin’s broader exposure to quantum threats.
Bitcoin’s larger quantum problem remains unresolved
This proof of concept emerges as institutional strategies increasingly account for quantum vulnerabilities.
An estimated 7 million BTC face potential vulnerability since their public keys are already exposed through legacy address formats, address reuse, or Taproot utilization. QSB offers no rescue mechanism for these specific assets.
Back in July, BlackRock, Coinbase, Strategy, and six other corporate entities established the Bitcoin Security Consortium, committing $15 million collectively over a three-year span toward Bitcoin security studies, which encompasses post-quantum cryptography. These participating organizations allocate their funds independently instead of through a shared pool.
Additionally, the US Treasury has incorporated digital assets into broader quantum-readiness initiatives for the financial sector.
As a result, Bitcoin confronts two distinct obstacles: designing migration options for users whose keys stay hidden and finding a protocol-level remedy for coins that are already exposed.
The Aug. 26 transaction demonstrates that a functional mainnet workaround exists for the initial problem. Meanwhile, the second challenge, impacting millions of Bitcoins, still demands a comprehensive solution.

